ISO27001
International standard.
The Delta platform’s Information Security Management System is certified to the ISO/IEC 27001 standard and audited periodically.
 Early Careers HiringWe identify capabilities and potential when professional experience is still limited.
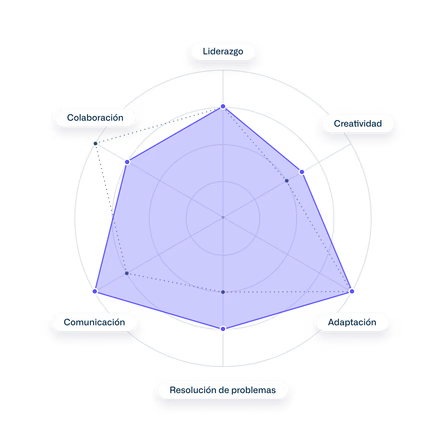 Manager HiringWe combine profile and business scenarios to test judgment and fit for positions of responsibility.
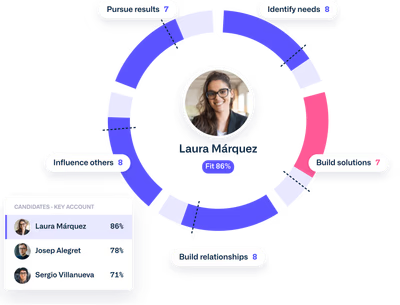 Sales HiringWe assess the capabilities involved in selling and how well they fit the demands of each role.
The Delta platform’s Information Security Management System is certified to the ISO/IEC 27001 standard and audited periodically.
Compliance with the General Data Protection Regulation to protect the confidentiality of every person assessed.
Data and its replicas are hosted in data centers located in Europe, encrypted in transit and at rest.
Participants know when they are interacting with an AI, results are backed by evidence for each competency, and the final decision is always made by a person in the organization.
Automatic backups, data replicas in Europe and an incident recovery plan.
Single sign-on with the client’s identity provider, two-factor authentication and role-based permissions.
Psicosoft’s management approves and leads our Information Security Management System, certified to the ISO/IEC 27001 standard. That is why we are committed to:
Ensuring that information is only seen by those who should see it, that it is not altered and that it is available when needed.
Meeting our clients’ requirements and the legal requirements on information security, as well as those the organization subscribes to.
Identifying, assessing and controlling security risks, monitoring and tracking their levels.
Detecting and managing any security incident, informing affected clients without delay and applying the lessons learned to prevent it from happening again.
Working only with technology suppliers that meet high security standards, and monitoring them periodically.
Setting and reviewing security objectives every year, training our team and continuously improving the management system.
The organization carrying out the assessment is the data controller. Delta Platform acts as data processor: it processes the data only in accordance with the controller’s instructions and under the data processing agreement required by Article 28 GDPR.
With an Information Security Management System certified to the ISO/IEC 27001 standard, which defines the confidentiality, integrity and availability controls and is periodically reviewed and audited.
Only some tools, such as AI Challenge, use artificial intelligence. In those tools, participants know from the start that they are interacting with an AI, results are backed by evidence for each competency, and the organization must review each result before making a decision. AI-based tools are designed in accordance with the EU AI Act, and we provide each client with the documentation they need for their own compliance.
Yes. They can contact the organization that invited them to the assessment, and we give that organization the support it needs to handle each request for access, rectification, erasure or other rights.
Yes. Write to us from the contact page, stating what your supplier approval process requires, and our team will send you the relevant documentation.
We share the documentation with your organization, under a non-disclosure agreement where appropriate.
Need more information? Write to us at bs@psicosoft.com.